
SERVICES · GDPR · DPO
External DPO – Data Protection Officer
I provide independent data protection support at management level. I help identify risks, put responsibility in order, make sound decisions and respond effectively to breaches.
Over 20 years of experience · Data protection, technology and risk management · Work in Polish and English
WHEN IT STARTS
When is support needed
The starting point may be a formal obligation, a client expectation, a change inside the organization, or a situation in which the board needs an independent assessment and a clear division of responsibility.
No DPO appointed
The organization needs a formal appointment, or an assessment of whether the obligation arises at all.
A client or auditor requirement
A counterparty expects evidence of maturity, risk control and the way personal data is actually protected.
A breach or time pressure
A fast assessment of the situation, the risk, the obligations and the order of actions is needed.
Documentation does not match practice
Records, procedures and policies do not reflect the actual processes, systems or responsibilities.
Organizational or technological change
A new system, service, supplier or business model changes the risk and the way data is processed.
Responsibility is dispersed
Legal, HR, IT and the business each see a fragment, and the board receives no single independent recommendation.
COOPERATION MODELS
Choose the right cooperation model
The scope of the service follows the size of the organization, its risk, and whether what is needed is a one-off diagnosis, a formally held role, or support for an existing officer.
1
Starting point
GDPR and DPO function audit
A standalone service, or an orderly start to further cooperation. It covers an assessment of the situation, the main risks and the non-conformities.
Result: a picture of the situation, priorities for the board and process owners, and a recommendation of the right operating model.
2
Holding the role
External DPO
A formal appointment of an officer from outside the organization. It covers the independent role and contact with the supervisory authority and with data subjects.
Result: the role is filled and cooperation runs with the board, legal, compliance, HR, IT and security.
3
Supporting the team
Support for your current DPO
For an organization that already has an officer. Consultations, assessments, audits and help with difficult decisions.
Result: a second, independent opinion in matters where one person should not be left alone.
SCOPE OF SUPPORT
Scope of DPO support
The scope may cover formally holding the role of the officer, or selected areas of support. Priorities follow the risk and the way the organization actually works.
Advice for the board
Consultations, recommendations and support for decisions concerning data protection.
Risk and corrective actions
Risk analyses, setting priorities and oversight of the recommendations – also where data protection meets NIS2 and the local cybersecurity law.
Documentation and processes
Records, procedures, information obligations and consistency between documentation and practice.
New projects and DPIA
Data protection impact assessments, opinions on systems and services, and privacy by design.
Day-to-day support
Data subject rights, processing agreements, cooperation with suppliers, and training matched to the risk carried by each team.
Personal data breaches
An initial assessment of the situation, recommendations, and a decision on whether dedicated incident support is needed.
The role of the officer has to work in decisions, processes and crisis situations, not only in documentation.
1
Documentation is evidence that the system works
2
It does not replace a risk assessment or the officer’s involvement
HOW IT RUNS
How cooperation proceeds
Every stage ends with a specific finding, an owner and a next step.
STAGE 1
Diagnostic call
We briefly establish the context, the needs, the constraints and the expected result.
STAGE 2
Risk review
I put the main processes, obligations, risks and gaps in order.
STAGE 3
Audit or start of the service
I deliver the agreed scope and prepare the recommendations.
STAGE 4
Priorities and plan
We agree the order of actions, the owners, and how delivery will be checked.
STAGE 5
Ongoing support
I track the agreed actions, support decisions and update the recommendations as things change.
What the management board gains
Support is there to make decisions easier, not to add to the list of documents and formalities.
1
A clear picture of risk
The board receives information on risk, priorities and the areas that require a decision.
2
An independent assessment
Recommendations do not follow the interest of one department or of a solution vendor.
3
Access to an expert
A conversation is possible with someone who knows the context and can explain the consequences.
4
Readiness for an incident
The organization knows who acts, what information is needed, and how to run the response.
Where the role of the officer ends
Independence does not mean working alongside the organization. It means being able to present an honest assessment and to support the board in making informed decisions.
The officer
Monitors compliance, advises and gives opinions.
Presents an assessment also when it is inconvenient.
Handles contact with the authority and with data subjects.
The organization
Makes the decisions and answers for compliance.
Provides information on processes, systems and suppliers.
Appoints owners for tasks and keeps to the deadlines.
When an incident occurs. I help establish the first actions, bring together the perspectives of the officer, IT and the board, and decide what scope of further support is needed. The process itself is described on the Incidents and breaches page.
WHO DELIVERS IT
Knowledge that comes from practice
Data protection calls for understanding the law, the technology, the processes and management responsibility at the same time.
Over 20 years in technology
Practice with systems, processes, suppliers and the problems organizations actually have.
Audits and breach practice
Recommendations come from the analysis of events, projects and the way an organization works.
Complex organizations
Communication matched to the board, and cooperation with legal, compliance, HR and IT.
Polish and English
Work with documentation, teams and stakeholders in both languages.
DIRECT CONTACT WITH THE EXPERT
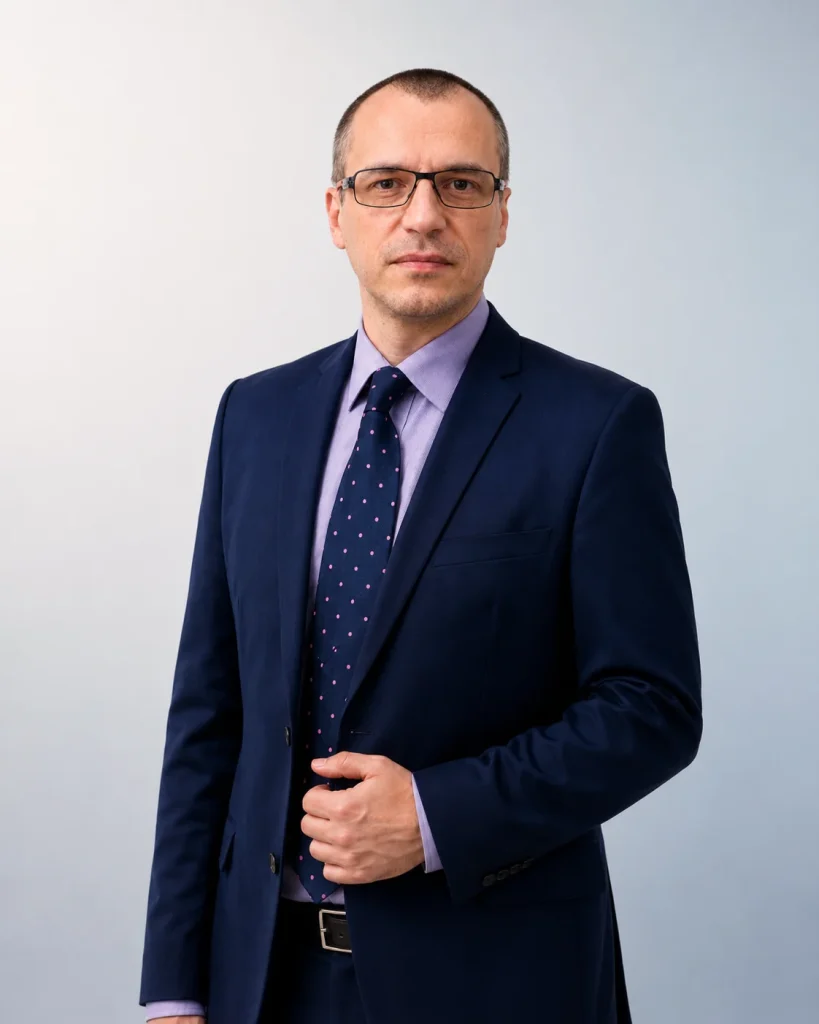
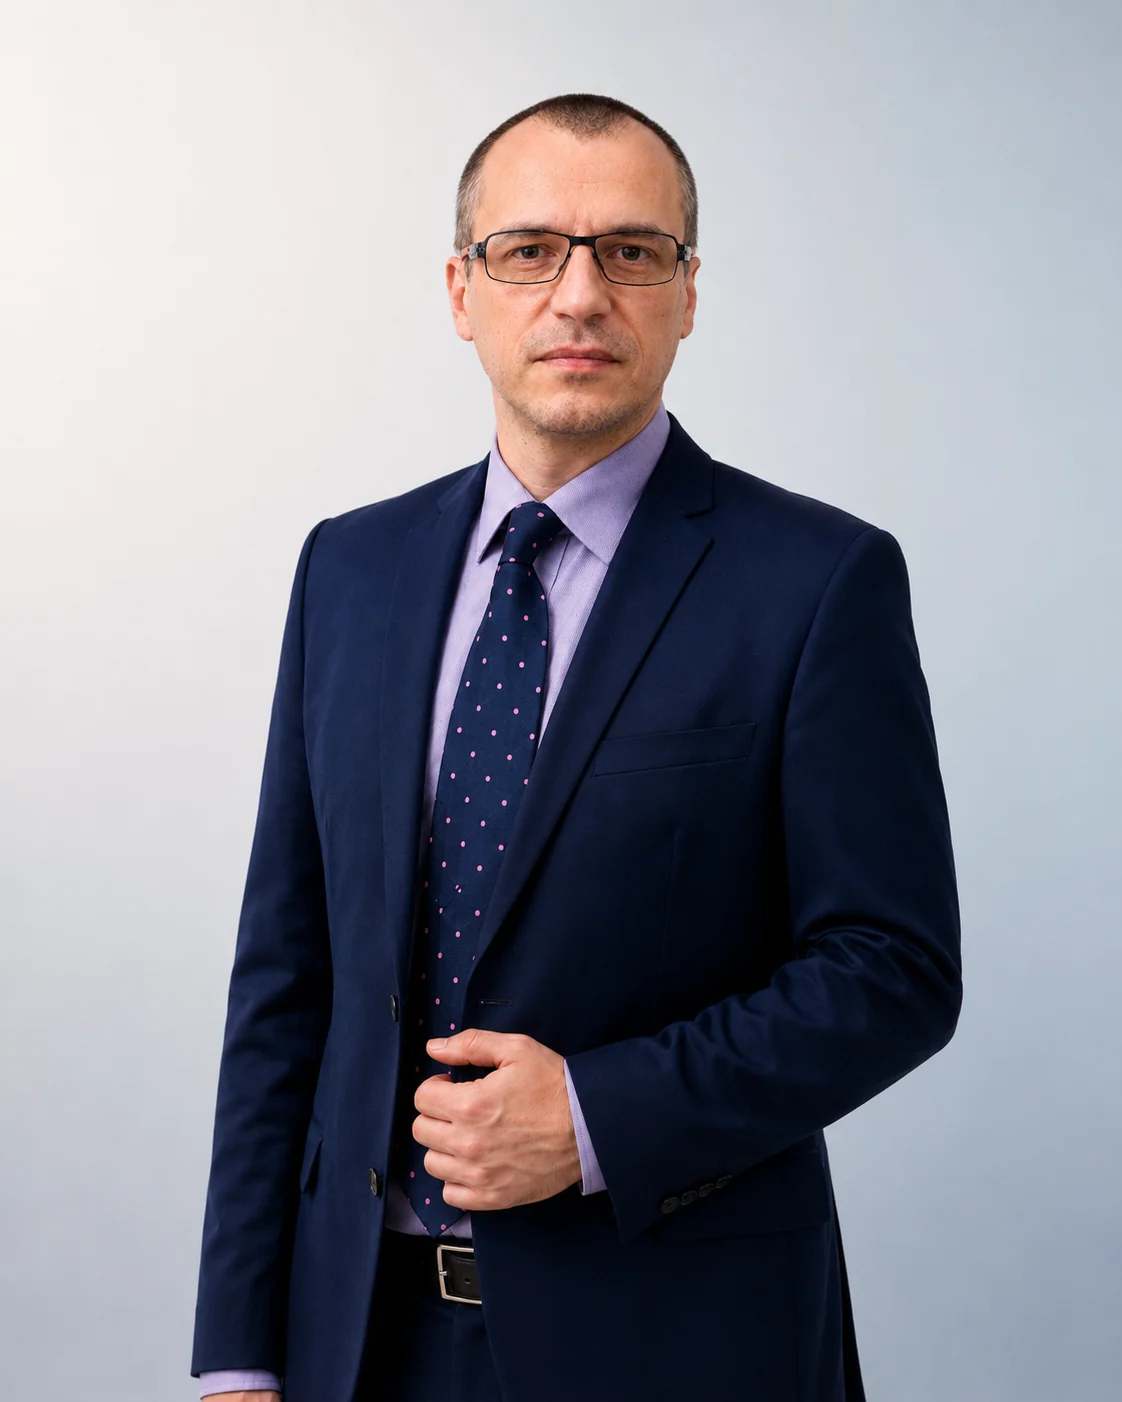
Michał Rutkowski
LabLogic — support and acting as DPO, preparation for NIS2 and the local law KSC, incident response, audits and training.
Frequently asked questions
Do we need a DPO if legal, HR or IT already handle data protection?
Those teams hold important roles, but they have their own tasks and their own interests. The officer should act independently, monitor compliance, advise, and be properly involved in matters concerning personal data. A first step may be to assess whether the organization is obliged to appoint one.
We already have GDPR documentation. Is an audit needed?
Documentation is one element of a data protection system. An audit shows whether it matches the actual processes, systems, responsibilities and risk, and whether the arrangements are really being applied.
Can we use the support without formally appointing a DPO?
Yes. If the organization is not obliged to appoint an officer, or already has one, advisory work, audits and ongoing expert support are possible without taking over the formal role.
How does an external DPO get to know the organization?
Cooperation starts with a diagnostic call, a review of the key processes and risks, and the identification of the people responsible. The context is filled in during consultations, audits and the delivery of the agreed actions.
Does an audit commit us to ongoing cooperation?
No. An audit can be a standalone project. Its result is a picture of the situation, a set of priorities and a recommendation for what to do next. The decision on the next stage belongs to the organization.
Does an external DPO take over the controller’s responsibility?
No. Responsibility for compliance and for decisions stays with the controller or the processor. The officer monitors, advises, gives opinions and supports the organization in making informed decisions.
Related services
Data protection meets three areas in which an organization usually already has its own rules and its own owners.
SERVICE
Cybersecurity
Organizations covered by NIS2 and the local cybersecurity law combine data protection duties with requirements on security and the supply chain.
SERVICE
Incidents and breaches
When a breach occurs, what counts is the order of actions, a safe flow of information, and a notification decision based on a documented risk assessment.
SERVICE
Training and workshops
The GDPR sets no training interval. Scope and format follow the roles and the risk carried by the team, and the adequacy of the programme must be demonstrable.
Related reading
The questions that keep coming back before the role of the officer is entrusted — answered from the wording of the GDPR.
KNOWLEDGE BASE
How to determine if an organization must appoint a DPO?
The three cases in Article 37(1) GDPR in which the obligation arises, and what a voluntary appointment brings with it.
KNOWLEDGE BASE
External or internal DPO? What to consider before deciding?
Article 37(6) GDPR prefers neither model — what decides are the conditions in which the role is performed, not the form of employment.
KNOWLEDGE BASE
What information should the board expect from the DPO?
Six things that add up to a picture of the state of data protection, instead of a report on activities carried out.
KNOWLEDGE BASE
How often should employees be trained on personal data protection?
The GDPR sets no interval — training is matched to risk and its adequacy must be demonstrable.
DIAGNOSTIC CALL
Let’s start with a conversation about your organization’s needs
We will establish whether the right first step is an audit, formally holding the role of the officer, ongoing expert support, or help with a breach.
This material is general and informational. It is not an individual legal opinion or a recommendation for a specific organization. The scope of obligations should be assessed in the light of its own situation.
BRIEFLY DESCRIBE YOUR SITUATION
The controller of the data provided in the form is Michał Rutkowski, trading as LabLogic Consulting. I use the data to handle the enquiry and prepare an answer or an offer. Details are set out in the Privacy Policy. Please do not send passwords, special categories of data or full incident documentation.