
MICHAŁ RUTKOWSKI
DPO, GDPR, NIS2 and cybersecurity for medium and large organizations
I help management boards and the teams responsible for data and security put risk, obligations and actions in order. I combine DPO and GDPR support, NIS2, incident handling and training.
New · free tool
An incident or a data breach? Check what to do now.
“I have an incident – what now?” is a free tool for the preliminary assessment of an incident in an organisation in Poland. In a few minutes you will see whether the event has to be notified and to whom, how much time you have and where to start. At the end, you can download an action plan as a PDF.
No account and no cookies
These deadlines may already be running
24 h
KSC
Early warning to the CSIRT
from detection of the significant incident
72 h
KSC
Significant incident notification
from detection of the significant incident
72 h
GDPR
Notification of the breach to the President of UODO (the Polish data protection authority)
from becoming aware of the breach, where feasible
The deadlines under the Polish KSC Act (implementing NIS2) apply to essential and important entities: already to former operators of essential services, and, as a rule, from 3 April 2027 to the others. The tool counts them from the time you enter.
What happened? Choose the closest match.


An employee gave away a password via a fake email
Phishing — is it already a notifiable incident?

Someone has taken over a mailbox or a Microsoft 365 account
Compromised account — who has to be notified?

A work laptop or phone has gone missing
Lost laptop with data — do I notify the President of UODO?

An email with personal data went to the wrong person
Email to the wrong person — is it a breach?


Something is wrong, but I don’t know what
You don’t need to know what the event is called. The tool asks, step by step, what happened, when it was detected, whose data is involved and whether you are covered by the KSC Act.
Deadlines that may already be running: 24 h and 72 h under the KSC Act, 72 h under the GDPR. The tool counts them from the time you enter.
The tool also answers questions such as
✓ No account and no cookies
✓ Action plan as a PDF
✓ Legal basis for every step
Practice since 2004
20+
years at the intersection of technology, data protection and risk management
Scope
GDPR · NIS2 · AI Act
three regimes handled as one matter for the organisation, not three separate projects
Role
External DPO
a function performed day to day, with documented decisions, not advice from a distance
Working languages
Polish and English
conversations with head office, group auditors and the local team without an interpreter
How can I help?
Choose the area that matches your organization’s current situation. If you are not sure where to start, a diagnostic conversation can be the first step.
DPO and GDPR
External DPO, support for your current data protection officer, a GDPR audit and ongoing advice for the board and the teams.
NIS2 and local law KSC
Qualification under NIS2 and the KSC act, gap and risk analysis, a plan and support for implementation and audit readiness.
Incidents and breaches
Assessment of the situation and the risk, decisions on notifications, communication and corrective actions.
Training and workshops
Practical GDPR, NIS2 and AI Act training for boards, senior management, employees and IT and compliance teams.
AI Act
AI Act — the obligations that took effect on 2 August 2026
2 February 2025
Prohibited practices and AI literacy
2 August 2025
General-purpose models, supervision and penalties
2 August 2026 · in force
Transparency (Article 50)
2 December 2026
End of the transition period
2 December 2027
High-risk systems (Annex III)
2 August 2028
AI in regulated products (Annex I)
The Digital Omnibus postponed the requirements for high-risk systems and left the transparency deadline unchanged. The Article 50 transparency duties have applied since 2 August 2026 and may cover chatbots, synthetic content and deepfakes. The scope depends on your role and the type of content, and the Article provides exceptions. I start from what is actually in use in the company, not from what the policy says should be there.
Where I start
- An inventory of AI systems — including the ones someone deployed without telling IT.
- Risk classification and a written justification for why a given system sits where it sits.
- Transparency obligations — notices, labelling of content, documentation.
- Team competence (Article 4) and preparation for December 2027.
When is it worth talking?
It is worth talking when obligations, risk or business expectations need to be put in order and turned into concrete decisions.
You don’t need a ready diagnosis
A general description of the situation is enough to start, with no confidential information. Together we will establish whether you need a consultation, an audit, an implementation project or ongoing support.
External DPO
The organization needs an external DPO or additional support for its current data protection officer.
NIS2 and local law KSC
The scope of obligations has to be established and the requirements translated into responsibility and a plan of action.
Incident or breach
An event has occurred, or there is a suspicion of a personal data breach.
AI systems in the organization
AI tools are already in use and nobody can say where, on what basis and who is responsible for them.
Documentation vs. practice
Documentation does not reflect the actual processes, systems or responsibilities.
Client requirements
A client, a contractor or an auditor expects confirmation of how data is protected or what the level of security is.
How does cooperation work?
Cooperation is structured, predictable and adjusted to the real risk and to the way the organization works.
STEP 1
Situation assessment
A short conversation, gathering the context and identifying the most important needs, risks and constraints.
STEP 2
Scope and priorities
Establishing responsibilities, expected results, a schedule and the order of actions.
STEP 3
Implementation
An audit, analysis, consultations, preparation of documentation, implementation or incident handling, depending on the agreed scope.
STEP 4
Maintenance and support
Checking that the arrangements are carried out, supporting the board and updating the solutions as the organization and the legal environment change.
Experience in complex organizations
Selected organizations I have supported or worked with. The scope of the individual projects varied.

Selected experiences
The examples show the way I work — from assessing the situation and the risk, through putting decisions in order, to implementing specific actions.
Handling a breach and notification to the supervisory authority
Situation
A serious incident requiring a fast risk assessment and a decision on notifying the supervisory authority.
Action
Analysis of the event, preparation of documentation, support for communication, notification to the authority and a corrective action plan.
Result
An orderly response by the organization, documented decisions and measures in place to limit the risk of recurrence.
Consistent data management in a capital group
Situation
Dispersed systems, inconsistent records and local processes that had to be reconciled with group standards.
Action
An inventory of assets, assignment of owners, clean-up of the records and linking the documentation to the actual processes.
Result
Clear responsibility, a consistent picture of processing and a basis for audits and group reviews.
Preparing the organization for NIS2 and KSC
Situation
An organization operating within an international group needed the NIS2 and KSC requirements translated into specific obligations, roles and priorities.
Action
Qualification of the scope, gap and risk analysis, a map of responsibilities and a practical implementation plan.
Result
The board received an orderly picture of the obligations, a schedule of actions and a basis for monitoring delivery.
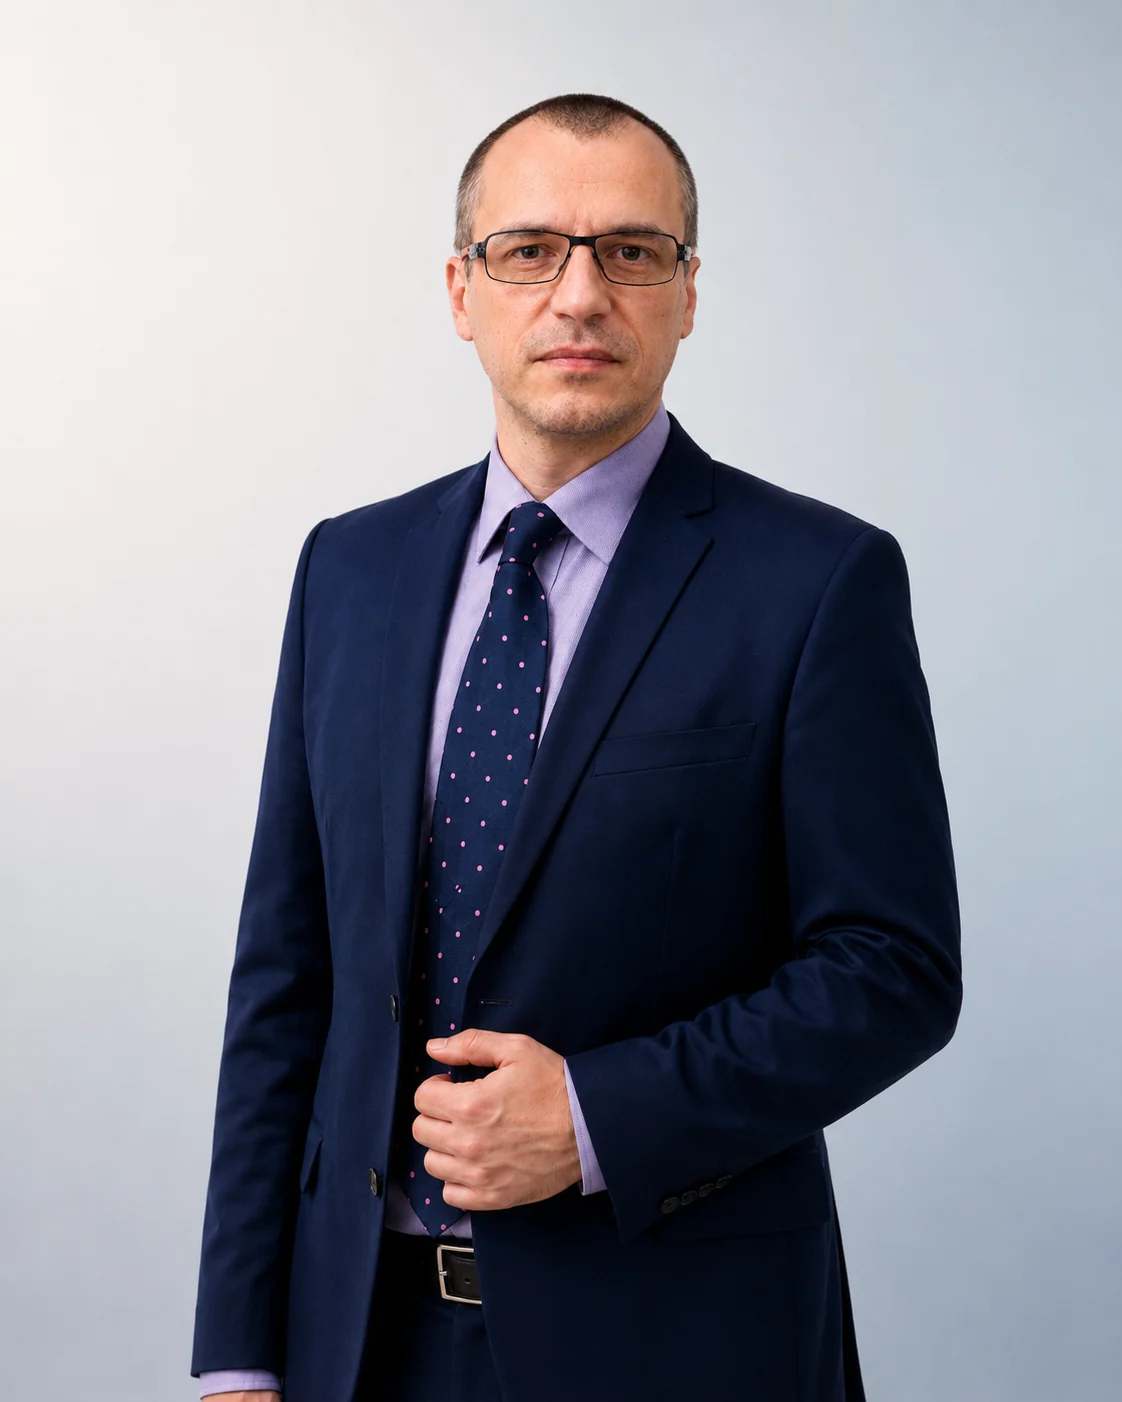
Michał Rutkowski
Since 2004 I have combined technology experience with personal data protection and cybersecurity. I act as a DPO, run audits and implementations, and support organizations in situations that call for a risk assessment, clear responsibilities and documented decisions.
I work with medium and large organizations, including those belonging to international capital groups. I connect legal and group requirements with the real processes, systems, resources and operational capabilities of the organization.
I combine perspectives crucial for organizations
Board and senior management
Responsibility, risk and priorities.
IT and security
Systems, safeguards and corrective actions.
Legal and compliance
Compliance, documentation and auditability of decisions.
Companies in capital groups
Local requirements, headquarters standards and cooperation between departments.
Let’s talk about the situation in your organization
Briefly describe your needs. Once I have reviewed the information, I will propose the right first step and — if the scope is a good fit — a date for a diagnostic conversation.
m.rutkowski@lablogic.pl
81-327 Gdynia, ul. Wolności 15/6, Poland
What happens after submitting the form
Review of your enquiry
I will read the description of the situation and assess which first step is the most appropriate.
Agreeing the scope
If the subject matches the support I provide, I will propose a diagnostic conversation or a specific form of cooperation.
Secure exchange of information
Confidential materials and incident details are shared only after we agree on a suitable communication channel.
Briefly describe your organization’s situation
The controller of the data provided in the form is Michał Rutkowski, operating as LabLogic Consulting. I use the data to handle your enquiry and to prepare an answer or an offer. Details are set out in the Privacy policy. Please do not send passwords, special categories of data or full incident documentation.